
5 October, 2026
ISO 27001 Training in Nigeria: PECB Lead Auditor Certification, Cost & Career Guide 2026
ISO 27001 Training in Nigeria: How to Become a PECB ISO 27001 Lead Auditor
Information is one of the most valuable things a business holds. Customer records, employee data, financial information, intellectual property, passwords and business documents can all become a serious risk when they are not properly protected. That is why information security is no longer only an IT concern.
If you are searching for ISO 27001 training in Nigeria, an information security certification that can strengthen your audit, governance, risk or compliance career, or the best information security certifications in 2026, this guide explains where ISO/IEC 27001 fits and how the PECB Lead Auditor route can help you build practical auditing capability.
What Is Information Security?
Information security is the practice of protecting information from unauthorised access, misuse, alteration, loss or disruption. It is commonly understood through three core objectives: confidentiality, integrity and availability.
In a real organisation, information security is not simply about installing antivirus software or putting up a firewall. It also involves people, policies, processes, risk management, controls and continual improvement. ISO/IEC 27001 provides a structured management-system approach for doing this.
What Is ISO 27001?
ISO/IEC 27001:2022 is the internationally recognised standard for an Information Security Management System (ISMS). It sets requirements for establishing, implementing, maintaining and continually improving an ISMS and uses a risk-based approach to managing information-security risks.
The important distinction is this: ISO 27001 is not simply a cybersecurity tool or a checklist. It is a management system that helps an organisation understand its information-security risks and put appropriate processes and controls around them.
What Does an ISO 27001 Lead Auditor Do?
An ISO 27001 Lead Auditor evaluates whether an organisation’s Information Security Management System meets the applicable requirements and whether the system is working effectively. The role can involve planning audits, collecting and evaluating evidence, identifying nonconformities, leading audit teams, reporting findings and following up on corrective actions.
- Plan and prepare ISO/IEC 27001 audits.
- Apply recognised audit principles, methods and techniques.
- Evaluate evidence against ISMS requirements.
- Identify and document audit findings and nonconformities.
- Lead audit teams and manage the audit lifecycle.
- Prepare clear audit reports and communicate findings.
- Support continual improvement of an organisation’s information-security management system.
What Are the Benefits of an Information Security Certification?
The value of an information security certification depends on the credential and the work you want to do. For professionals interested in auditing, governance, risk and compliance, ISO 27001 can add a management-system perspective that purely technical certifications do not provide.
- Demonstrates structured knowledge of information-security management and auditing.
- Strengthens your professional profile for audit, GRC, compliance and information-security roles.
- Builds practical understanding of audit planning, evidence, findings and corrective action.
- Helps professionals communicate information-security risks in a business context.
- Can support progression into internal audit, external audit, ISMS, risk and compliance work.
- Adds an internationally recognised framework to your professional development.
What Are the Best Information Security Certifications in 2026?
There is no single ‘best’ information security certification for everyone. The right choice depends on the job you want. A technical security professional may choose a different path from an auditor, risk professional or information-security manager.
Certification | Strongest fit | Why consider it |
ISO 27001 Lead Auditor | ISMS audit, GRC, compliance | Strong choice for professionals who want to audit and evaluate information-security management systems. |
CISSP | Senior cybersecurity/security management | Broad security leadership and architecture coverage; generally suited to experienced security professionals. |
CISA | IT audit, assurance and governance | Strong fit for IT audit and assurance professionals. |
CEH | Ethical hacking / security testing | More focused on offensive security and penetration-testing concepts. |
CompTIA Security+ | Foundational cybersecurity | Useful entry-level foundation for people beginning a technical cybersecurity pathway. |
If your goal is specifically to audit an Information Security Management System, ISO 27001 Lead Auditor is the more directly aligned choice. That is why it is especially relevant to internal auditors, compliance professionals, risk managers, IT managers, consultants and information-security practitioners.
Why Choose PECB ISO 27001 Lead Auditor Training?
PECB’s ISO/IEC 27001 Lead Auditor training is designed to develop the knowledge and skills needed to perform an ISMS audit using recognised auditing principles, procedures and techniques. The PECB pathway is therefore particularly relevant to professionals who want a formal route into ISO 27001 auditing rather than only an awareness-level understanding of information security.
What Will You Learn in the Training?
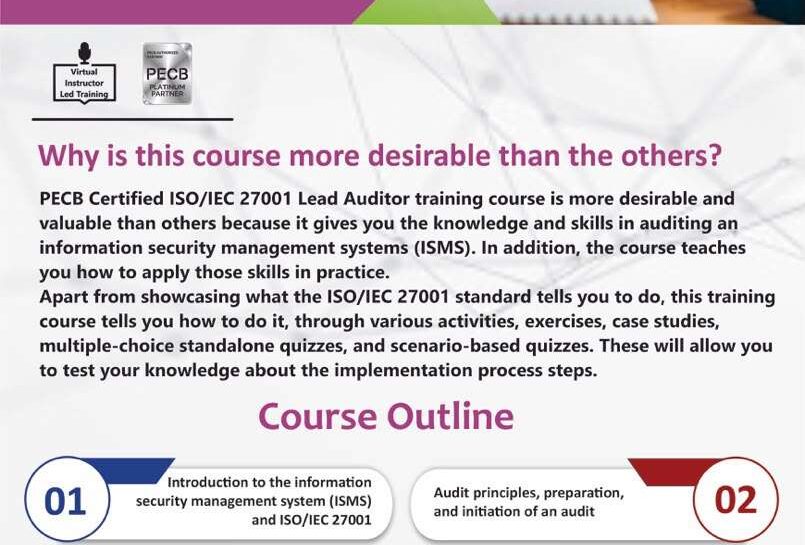
- Introduction to the Information Security Management System (ISMS) and ISO/IEC 27001.
- Audit principles, preparation and initiation of an audit.
- On-site audit activities and evidence gathering.
- Closing the audit and communicating audit results.
- Practical activities, exercises, case studies and scenario-based questions.
- How to apply auditing knowledge rather than simply memorising the standard.
Who Should Take ISO 27001 Lead Auditor Training?
- Information Security Managers and Officers
- Internal and external auditors
- IT Managers and Systems Administrators
- Risk, Governance and Compliance professionals
- Consultants working with information-security management systems
- Quality and management-system professionals
- Professionals responsible for maintaining or auditing an ISMS
- Professionals planning a career in information-security auditing
How Much Is ISO 27001 Lead Auditor Training in Nigeria?
For the October 2026 PECB cohort advertised by Training Heights, the training fee is ₦250,000. The exam fee shown on the course flyer is $400.
Course | PECB ISO/IEC 27001:2022 Lead Auditor |
Training dates | 26–29 October 2026 |
Delivery | Virtual Instructor-Led Training |
Training fee | ₦250,000 |
Exam fee | $400 |
Provider | Training Heights |
Why Take ISO 27001 Training With Training Heights?
Training Heights provides instructor-led professional certification training for individuals and organisations. For this PECB ISO 27001 Lead Auditor cohort, the focus is not simply on reading the standard; the course is structured around audit principles, practical activities, case studies and scenario-based learning.
If you are comparing ISO 27001 training providers in Nigeria, the practical question is not only ‘Who is cheapest?’ It is whether the programme gives you the knowledge, structure and support needed to understand how an ISMS audit actually works.
ISO 27001 Lead Auditor vs Lead Implementer: Which One Is Right for You?
Lead Auditor | Lead Implementer | Choose based on your goal |
Audits an ISMS | Builds and manages an ISMS | Audit, assurance, GRC or compliance → Lead Auditor |
Evaluates evidence and findings | Plans, implements and improves controls/processes | Implementation or ISMS management → Lead Implementer |
Focuses on audit lifecycle | Focuses on implementation lifecycle | You can later build both skill sets as your career develops |
Frequently Asked Questions About ISO 27001 Training in Nigeria
What is ISO 27001 certification?
ISO/IEC 27001 is the international standard for an Information Security Management System. Organisations can undergo an independent certification process to demonstrate that their ISMS meets the standard’s requirements. Individual professionals can take ISO 27001 training and pursue professional certification through an appropriate certification scheme.
Is ISO 27001 a cybersecurity certification?
It is closely related to cybersecurity, but its scope is broader than technical cybersecurity alone. ISO 27001 focuses on managing information-security risks through people, processes, technology and organisational controls.
Is ISO 27001 useful for a career in information security?
Yes, particularly for people interested in information-security governance, risk, compliance, auditing and ISMS work. It is not a replacement for hands-on technical security skills where a job requires them.
How do I become an ISO 27001 Lead Auditor?
Take a suitable ISO/IEC 27001 Lead Auditor training programme, develop the required auditing knowledge and complete the applicable examination and certification requirements of the certification body. Training Heights is offering a PECB ISO/IEC 27001:2022 Lead Auditor cohort on 26–29 October 2026.
How much does ISO 27001 Lead Auditor training cost in Nigeria?
Training Heights’ October 2026 PECB cohort is advertised at ₦250,000 for training, with a separate $400 exam fee shown on the course flyer.
Is PECB ISO 27001 Lead Auditor recognised?
PECB offers an ISO/IEC 27001 Lead Auditor certification pathway and describes the course as developing expertise to perform ISMS audits using recognised audit principles, procedures and techniques. Check the current PECB certification requirements before enrolment.
Can a beginner take ISO 27001 Lead Auditor training?
It depends on the learner’s background and the certification requirements. People new to ISO management systems can learn the fundamentals, but prior exposure to information security, auditing, risk, IT or management systems can make the course easier to apply.
What is the difference between ISO 27001 and ISO 27002?
ISO/IEC 27001 specifies requirements for an Information Security Management System. ISO/IEC 27002 provides guidance and best-practice information-security controls. They complement each other but serve different purposes.
Which is better: ISO 27001 Lead Auditor or CISSP?
Neither is universally better. CISSP is broader and aimed at experienced cybersecurity/security professionals, while ISO 27001 Lead Auditor is more directly aligned with ISMS auditing, governance, risk and compliance work. Choose based on the role you want.
Ready to Start Your ISO 27001 Lead Auditor Journey?
Training Heights’ PECB ISO/IEC 27001:2022 Lead Auditor training runs 26–29 October 2026. The advertised training fee is ₦250,000, with a $400 exam fee. If you want to build practical information-security auditing skills and position yourself for ISMS, audit, risk and compliance opportunities, contact Training Heights to confirm availability and enrol.
Training Heights | +234 806 726 9749 | victoria.oyedeji@trainingheights.com
📞 Spots are limited – don’t miss out!
Ready to Learn?
Take the next step in your career with this course. Enhance your skills today.
🎥 Virtual, instructor-led sessions – Learn from the best, wherever you are.
🌍 Globally recognized certifications – Boost your credibility worldwide.
🕒 Flexible schedules – Learn at your convenience.
🧑🏫 Expert trainers & hands-on learning – Real skills, real impact.
💰 Affordable pricing & group discounts – Learn more, save more.